Protecting Against ShinyHunters: Advanced Cyber Threats and DPRM Solutions

Learn how ShinyHunters exploit vulnerabilities and how Certes DPRM protects your organisation with advanced data security, encryption, and segmentation.

Protecting Against ShinyHunters: Advanced Cyber Threats and DPRM Solutions

Cybersecurity threats are growing at an unprecedented rate, with hacking groups like ShinyHunters targeting data-rich organisations globally. Known for their high-profile data breaches, including a financial firm affecting 30 million records, ShinyHunters have cemented their reputation as a major threat to businesses across industries.

Certes understands the importance of safeguarding sensitive data and protecting organisations from these advanced cyber threats. Through a robust Data Protection and Risk Mitigation (DPRM) solution, Certes ensures that organisations stay one step ahead of malicious actors like ShinyHunters.

Who Are ShinyHunters and Why Are They a Threat?

ShinyHunters is a notorious hacking group that has targeted organisations across various industries, exploiting vulnerabilities to steal vast amounts of sensitive data. Their name has become synonymous with large-scale data breaches, with some of their most notable attacks affecting millions of records from financial institutions, healthcare providers, and online retailers.

What sets ShinyHunters apart is their sophisticated approach to cyberattacks. They often exploit poorly secured systems, gain unauthorised access to databases, and either sell the stolen data on the dark web or use it to extort organisations. For businesses, this results in reputational damage, regulatory fines, and significant financial losses.

Understanding the methods and motivations of ShinyHunters is crucial for organisations aiming to protect themselves. Their attacks are not random but calculated, targeting industries where data is most valuable, making them one of the most formidable threats in today’s digital landscape.

The Impact of ShinyHunters Attacks on Organisations

The consequences of a ShinyHunters attack extend far beyond the immediate loss of data. Organisations targeted by this hacking group often face devastating impacts, including:

  1. Data Theft: Sensitive customer and company information, such as financial details, personal identification, and trade secrets, is stolen, often leading to privacy violations and legal repercussions.
  2. Financial Losses: Beyond ransom payments or the loss of stolen funds, businesses suffer from operational downtime, regulatory fines, and the cost of rebuilding their systems and trust.
  3. Reputational Damage: Clients, partners, and stakeholders may lose confidence in the organisation’s ability to safeguard data, resulting in long-term damage to the brand and reduced customer loyalty.
  4. Operational Disruptions: ShinyHunters are known for infiltrating networks and causing widespread system outages, leaving organisations struggling to restore normal operations.

For data-rich industries, the stakes are particularly high. A single breach can cripple an organisation’s ability to function, demonstrating the urgent need for robust security measures to counter such advanced threats.

How Certes DPRM Defends Against ShinyHunters

Certes’ Data Protection and Risk Mitigation (DPRM) solution is specifically designed to counter sophisticated cyber threats like ShinyHunters. By focusing on data-centric security, Certes ensures that even if hackers infiltrate an organisation’s network, the data itself remains secure and inaccessible. Key features of Certes DPRM include:

  • Data Encryption: Sensitive information is encrypted both in transit and at rest, rendering it useless to attackers even if accessed.
  • Segmentation: Networks are segmented to limit an attacker’s ability to move laterally and access other areas of the system.
  • Access Control: Strict access policies ensure that only authorised users can interact with critical data, reducing the risk of insider threats or unauthorised escalations.

With Certes DPRM, organisations can mitigate the risk of a breach by deploying proactive measures that stop attackers in their tracks, offering peace of mind in a constantly evolving threat landscape.

Securing Data in Transit and at Rest

Data security is a critical component of any robust cybersecurity strategy, and Certes DPRM excels at protecting information both during transmission and in storage.

  • Data in Transit: ShinyHunters frequently target unencrypted data as it moves between systems. Certes DPRM employs advanced encryption protocols to ensure that sensitive data remains secure during transmission, safeguarding it from interception or tampering.
  • Data at Rest: Stored data is often a primary target for attackers. Certes DPRM secures information with powerful encryption algorithms and granular access controls, preventing unauthorised access even if attackers breach the network.

By securing data at every stage of its lifecycle, Certes DPRM eliminates vulnerabilities and ensures compliance with stringent industry regulations, offering a comprehensive defence against ShinyHunters and other advanced threats.

Preventing Escalated Privileges and Lateral Movement

One of the key tactics used by ShinyHunters and other sophisticated attackers is gaining escalated privileges to move laterally across networks. Once inside, they exploit vulnerabilities to access sensitive data and disrupt operations. Certes DPRM is designed to neutralise this threat through the following measures:

  • Role-Based Access Control (RBAC): Certes DPRM enforces strict access policies, ensuring users only have permissions necessary for their role. This limits the ability of attackers to elevate privileges and access critical systems.
  • Network Segmentation: By isolating sections of the network, Certes DPRM prevents attackers from moving freely once they breach a single system. Even if one area is compromised, the rest of the network remains secure.
  • Real-Time Monitoring: Certes DPRM continuously tracks user activity to identify and block unusual or unauthorised behaviour, stopping lateral movement before it causes damage.

These safeguards ensure that even if attackers penetrate the network perimeter, their ability to exploit the system is severely restricted, providing an essential layer of protection against escalating threats.

Protecting Active Directory Against Advanced Threats

Active Directory (AD) is a critical target for groups like ShinyHunters, as it controls access to an organisation’s systems and data. A compromised AD can grant attackers unrestricted access to sensitive resources, making its protection a top priority. Certes DPRM provides comprehensive safeguards for Active Directory, ensuring it remains secure against advanced threats:

  • Authentication Controls: Certes DPRM strengthens AD authentication processes by implementing multi-factor authentication (MFA) and enforcing strong password policies, reducing the risk of unauthorised access.
  • Privilege Management: AD users often have excessive permissions, which attackers can exploit. Certes DPRM limits privileges based on specific roles, ensuring minimal access is granted only as needed.
  • Monitoring and Alerts: Certes DPRM continuously monitors AD for suspicious activities, such as repeated login attempts or unauthorised privilege changes, triggering real-time alerts to address threats immediately.

By securing Active Directory, Certes DPRM protects the foundation of an organisation’s access management system, preventing attackers from gaining control and exploiting vulnerabilities.

Futureproofing Your Organisation Against Emerging Risks

As cyber threats continue to evolve, organisations must prepare for both current and future challenges. Groups like ShinyHunters are constantly adapting their tactics, and emerging risks such as quantum computing pose even greater threats to data security. Certes DPRM is designed to futureproof organisations by offering cutting-edge solutions that address these evolving dangers:

  • Advanced Encryption Standards: Certes DPRM uses encryption methods that are resistant to current and anticipated threats, including the potential risks posed by quantum computing.
  • Scalability: The solution grows with your organisation, ensuring that security measures remain effective as your infrastructure expands or evolves.
  • Proactive Updates: Certes regularly updates its DPRM solution to address new vulnerabilities and emerging attack methods, keeping your organisation ahead of the curve.

By investing in a forward-thinking security solution like Certes DPRM, organisations can reduce their exposure to future risks and build a resilient defence strategy that withstands the test of time.

Learn More About Certes DPRM Solutions

Protecting your organisation against advanced threats like ShinyHunters requires more than just awareness—it demands proactive action and robust solutions. Certes DPRM offers a comprehensive approach to data protection, combining encryption, segmentation, and advanced access controls to safeguard your most valuable assets.

With Certes, you can ensure your organisation is equipped to withstand current and emerging threats, maintain compliance with industry regulations, and build a secure foundation for future growth.

Take the next step in securing your data and systems. Request a demo today to discover how Certes DPRM can protect your organisation against ShinyHunters and other cyber threats.
Go deeper

Practical resources on this subject.

Browse all resources
  • Executive Liability Is Real: Why Data Protection Now Sits in the Boardroom

    Blog

    Executive Liability Is Real: Why Data Protection Now Sits in the Boardroom

    If your organization mishandles sensitive data, regulators will knock on the boardroom door – and you could be personally liable. It’s time to stop securing the castle and start protecting the crown jewels: your data.

    Feb 2026

  • Why Your Cybersecurity Strategy Is Failing Where It Matters Most

    Blog

    Why Your Cybersecurity Strategy Is Failing Where It Matters Most

    If your business still believes perimeter defenses will protect it from a breach, you're already exposed. Most security strategies are focused on the wrong target, and it’s costing companies millions in fines, downtime, and lost trust.

    Feb 2026

  • It’s the Most Wonderful Time of the Year… Unless You’re Hit by Ransomware

    Blog

    It’s the Most Wonderful Time of the Year… Unless You’re Hit by Ransomware

    Holiday season means peak revenue for retailers, and peak opportunity for ransomware gangs. With attacks spiking and downtime more costly than ever, protecting the perimeter isn’t enough. Certes DPRM secures data in transit across every system and partner, keeping transactions flowing and customer trust intact when it matters most.

    Nov 2025

  • Why Data Breach Damage Runs Deeper Than You Think

    Infographic

    Why Data Breach Damage Runs Deeper Than You Think

    The headlines cover the breach. But what really brings companies down happens beneath the surface—regulatory fines, executive fallout, customer churn, and shareholder lawsuits. Jaguar Land Rover lost £1.9 billion. M&S dropped £1 billion in market value. These go beyond the headlines; they’re business-ending events. Discover how DPRM can help reduce your risk, protect your data, and avoid becoming the next headline.

    Nov 2025

  • Boardroom Cybersecurity: Why Liability Has Shifted to Executives

    Blog

    Boardroom Cybersecurity: Why Liability Has Shifted to Executives

    There was a time when a data breach was an IT problem. Those days are gone. Today, cybersecurity has climbed the corporate ladder right to the top floor.

    Oct 2025

  • Why Your Service Provider’s Breach Is Your Problem

    Blog

    Why Your Service Provider’s Breach Is Your Problem

    Too many CFOs and CISOs still believe their service providers have security under control. They don’t.

    Oct 2025

  • The Hidden Cost of Holding Customer Data: Why CFOs Should Rethink Their Risk Approach

    Blog

    The Hidden Cost of Holding Customer Data: Why CFOs Should Rethink Their Risk Approach

    In holding customer data, you also hold the liability if it’s compromised. What if you could reduce this liability, without impacting your service delivery?

    Sep 2025

  • Scattered Spider: How Certes DPRM Could Have Broken the Attack Chain

    Blog

    Scattered Spider: How Certes DPRM Could Have Broken the Attack Chain

    We explain how Certes DPRM would have neutralized the recent Scattered Spider retail ransomware attacks, and why a new approach to data security is needed

    Aug 2025

  • How Service Providers Can Eliminate Data Liability Without Losing Functionality

    Blog

    How Service Providers Can Eliminate Data Liability Without Losing Functionality

    When businesses talk about performance, the conversation is usually about uptime, speed, and scalability. But none of that matters when trust is broken. When customer data is exposed, systems are breached, and liability lands squarely on your balance sheet.

    Jun 2025

  • Why Your Firewall Can’t Stop a Lawsuit: The Real Risk of Ignoring Data Protection

    Blog

    Why Your Firewall Can’t Stop a Lawsuit: The Real Risk of Ignoring Data Protection

    Cybersecurity strategy has typically revolved around a single principle for too long: keep the bad guys out.

    Jun 2025

  • Data Poisoning: The Hidden Threat That Could Kill Your AI

    Blog

    Data Poisoning: The Hidden Threat That Could Kill Your AI

    AI is only as good as the data it learns from, and attackers are already exploiting that fact. Data poisoning is quickly becoming one of the most dangerous and least understood cyber threats facing organizations. While your security team focuses on perimeter defenses, attackers are poisoning the data your AI relies on – without ever needing to break into your systems. But what Is Data Poisoning? And Why Should You Care?

    Apr 2025

  • Data Is the Target: Why Perimeter Security Alone Is Not Enough

    Blog

    Data Is the Target: Why Perimeter Security Alone Is Not Enough

    Ransomware recovery is costly, and the reputational damage that follows can be irreparable. And it’s not just companies paying the price – executives face personal liability for failing to protect sensitive data. So why do so many businesses continue to rely on outdated network security models that focus solely on perimeter defenses?

    Feb 2025

  • Beyond Ransomware Payments: A Proactive Approach to Cybersecurity

    Blog

    Beyond Ransomware Payments: A Proactive Approach to Cybersecurity

    The UK government's recent proposal to ban public sector bodies – including the NHS, schools, and local councils – from making ransomware payments appears to send a strong message, but it only scratches the surface of what’s needed to counter these attacks.

    Jan 2025

  • Trust but Verify: Strengthening AI Security with Data Protection

    Blog

    Trust but Verify: Strengthening AI Security with Data Protection

    Research reveals an alarming vulnerability in AI systems, and their susceptibility to jailbreaking, highlighting the need to secure the data that underpins AI.

    Dec 2024

  • Breaking the Kill Chain: How DPRM Prevents Active Directory Breaches Before They Happen

    Blog

    Breaking the Kill Chain: How DPRM Prevents Active Directory Breaches Before They Happen

    Active Directory (AD) is a priority target for ransomware attacks. We explore why organisations need to adopt a new approach to protecting their systems. By breaking the kill chain, we can stop attacks in their tracks – protecting the data rather than relying solely on network-based defenses.

    Sep 2024

  • Rethinking Cybersecurity in Critical Infrastructure

    Blog

    Rethinking Cybersecurity in Critical Infrastructure

    The energy sector remains a prime target for cyber attackers seeking to disrupt global economies. Recent examples, such as the Halliburton incident, highlight how criminals can exploit vulnerabilities that persist in systems, like Active Directory (AD) – underscoring the urgent need for a shift in how we approach cybersecurity for critical infrastructure.

    Sep 2024

  • Once More into the Breach, Episode 2: The Critical Role of the C-Suite in Data Protection

    Video

    Once More into the Breach, Episode 2: The Critical Role of the C-Suite in Data Protection

    From GDPR to PCI compliance, regulatory bodies are tightening their grip, holding C-suite executives personally accountable for data breaches. With fines reaching millions and the spectre of potential imprisonment, the stakes have never been higher for both data protection and risk mitigation strategies.

    Jul 2024

  • Protecting Against ShinyHunters: Advanced Cyber Threats and DPRM Solutions

    Blog

    Protecting Against ShinyHunters: Advanced Cyber Threats and DPRM Solutions

    Cyber threats in data-rich industries are growing. A breach affecting 30 million at a financial firm by ShinyHunters highlights the need for robust Data Protection and Risk Mitigation solutions.

    Jul 2024

  • Going on the Offensive: Tackling Volt Typhoon Attacks Webinar

    Webinar

    Going on the Offensive: Tackling Volt Typhoon Attacks Webinar

    Simon Hill, VP North America and Lorilee Ressler, Solutions Architect provide an overview of the rising IT attacks on critical infrastructure operators and how Volt Typhoon continues to compromise systems all over the globe. They present the use case for how Typhoon attacks can be addressed and prevented as well as an overview on how

    May 2024

  • Ransomware Attacks on Active Directory: A Call to Action

    Blog

    Ransomware Attacks on Active Directory: A Call to Action

    In recent years, ransomware attacks surged, threatening businesses globally. A troubling trend is the targeted attack on Active Directory (AD), a crucial network component. We'll explore global ransomware attacks, tactics by groups like AlphaV/BlackCat and Volt Typhoon, shortcomings of traditional defenses, and introduce Certes DPRM as a proactive solution.

    May 2024

  • Understanding and Mitigating Volt Typhoon Attacks

    Blog

    Understanding and Mitigating Volt Typhoon Attacks

    Organisations worldwide are facing a new era of cyber threats, in recent months news has broke that numerous critical infrastructure operators have had their IT systems compromised by Volt Typhoon. We delve into the nuances of Volt Typhoon attacks, share the implications they can have for organisations and the practical strategies to adapt and innovate

    Mar 2024

  • The Legal Liability Dilemma

    Blog

    The Legal Liability Dilemma

    How do security leaders navigate the aftermath of a data breach? In the rapid pace of today’s digital landscape, data breaches have become an unfortunate reality for organisations worldwide. As these incidents continue to rise, a growing concern among security leaders, particularly Chief Information Security Officers (CISOs), revolves around their legal liability following such breaches.

    Jul 2023

  • Data Breach Accountability: Who Foots the Bill?

    Blog

    Data Breach Accountability: Who Foots the Bill?

    News stories about cybersecurity data breaches are sometimes difficult to avoid and even more difficult to digest. Data is increasingly valuable to businesses – especially data related to customers, payments and of a sensitive nature.

    Dec 2022

  • Active Directory Protection: Breaking the Ransomware Kill Chain

    Solution Brief

    Active Directory Protection: Breaking the Ransomware Kill Chain

    Certes provides a comprehensive approach to Active Directory protection, focusing on disrupting the ransomware "Kill Chain" at its most vulnerable point: privilege escalation and lateral movement. Data Protection and Risk Mitigation (DPRM) separates data access from network access, preventing lateral movement within the network and using quantum cryptography to secure sensitive information.

  • Volt Typhoon Attacks on Active Directory

    Whitepaper

    Volt Typhoon Attacks on Active Directory

    Volt Typhoons activities are challenging to identify and respond to due to the actor’s primary method of attack, “Living off the Land”, which leverages legitimate tools and functionalities already present within a compromised system or network to carry out malicious activities. Rather than relying on conspicuous malware or custom tools that may trigger security alerts,

  • Certes DPRM: Breaking the Kill Chain

    Infographic

    Certes DPRM: Breaking the Kill Chain

    This infographic breaks down the ransomware kill chain and shows how Certes’ Data Protection & Risk Mitigation (DPRM) solution disrupts attacks before they cause damage. By devaluing data with quantum-grade encryption, blocking privilege escalation, and preventing exfiltration, Certes renders stolen data useless – stopping ransomware in its tracks.

  • Breaching the Energy Sector: Protecting Critical Infrastructure Against Advanced Cyber Exploits

    Whitepaper

    Breaching the Energy Sector: Protecting Critical Infrastructure Against Advanced Cyber Exploits

    Sophisticated attacks like those on Halliburton show that organizations can no longer solely rely on perimeter-based security. A proactive, multi-layered defense is essential to thwart these evolving threats. DPRM can serve as a proactive defense mechanism, limiting attackers’ ability to exploit vulnerabilities like ZeroLogon, thereby ensuring the integrity and security of your organization’s critical assets.
  • Addressing the Critical Threat of ShinyHunters: How DPRM Can Protect Against Advanced Cyber Attacks

    Whitepaper

    Addressing the Critical Threat of ShinyHunters: How DPRM Can Protect Against Advanced Cyber Attacks

    The recent breach hitting a leading financial services company, affecting 30 million individuals, underscores the critical threat posed by sophisticated hacking groups such as ShinyHunters. This attack, part of a worrying trend, highlights the increased targeting of the financial services sector, which holds vast amounts of sensitive data. The hacker’s newsworthy breaches are a stark

  • Hope Is Not a Strategy: Rethinking Data Protection in the Age of Zero-Day Attacks

    Whitepaper

    Hope Is Not a Strategy: Rethinking Data Protection in the Age of Zero-Day Attacks

    The frequency of zero-day vulnerabilities is increasing, with 97 exploits in 2023, up from 62 in the previous year. Our whitepaper discusses the necessary shift in cybersecurity, emphasising the need to protect data against rising zero-day threats. It argues against relying solely on perimeter-based security and advocates for a proactive, zero-trust data access approach for
  • Certes for Federal Agencies

    Infographic

    Certes for Federal Agencies

    Federal systems are under relentless attack — from foreign adversaries, insider threats, and zero-day exploits. Even with cloud-first strategies, endpoint controls, and zero trust architectures, attackers are logging in — not breaking in. Certes DPRM protects what others can’t see.
  • Why Don't Companies Take Data Loss More Seriously?

    Whitepaper

    Why Don't Companies Take Data Loss More Seriously?

    Network breaches and Ransomware attacks are happening daily across all verticals and against both large and small companies, but why? Surely these companies are following the best practise and deploying the latest recommended network security and monitoring? When you map the rise in breaches against the introduction of technology designed to stop them we can see that the traditional approach of perimiter-based security measures is not working to stop or even slow the rate of breaches.
  • Why Data Security Is More Important Than Network Security

    Whitepaper

    Why Data Security Is More Important Than Network Security

    The realisation that data security is the most critical aspect of cybersecurity is now a staple - it’s now far more important than traditional network security. While network security plays a role in protecting the infrastructure, it is ultimately data that cybercriminals, insider threats, and nation-state actors are after. Securing the network without securing the data is like locking the doors but leaving the valuables unguarded.

  • Why Protecting Data Itself Is the Key to Defeating Zero-Day Attacks

    Whitepaper

    Why Protecting Data Itself Is the Key to Defeating Zero-Day Attacks

    In today’s digital age, cybersecurity threats are evolving at an unprecedented pace, with zero-day attacks standing out as some of the most formidable challenges for security professionals. While network monitoring tools play a crucial role in detecting anomalies and responding to known threats, they are fundamentally incapable of providing full protection against data loss stemming from zero-day attacks

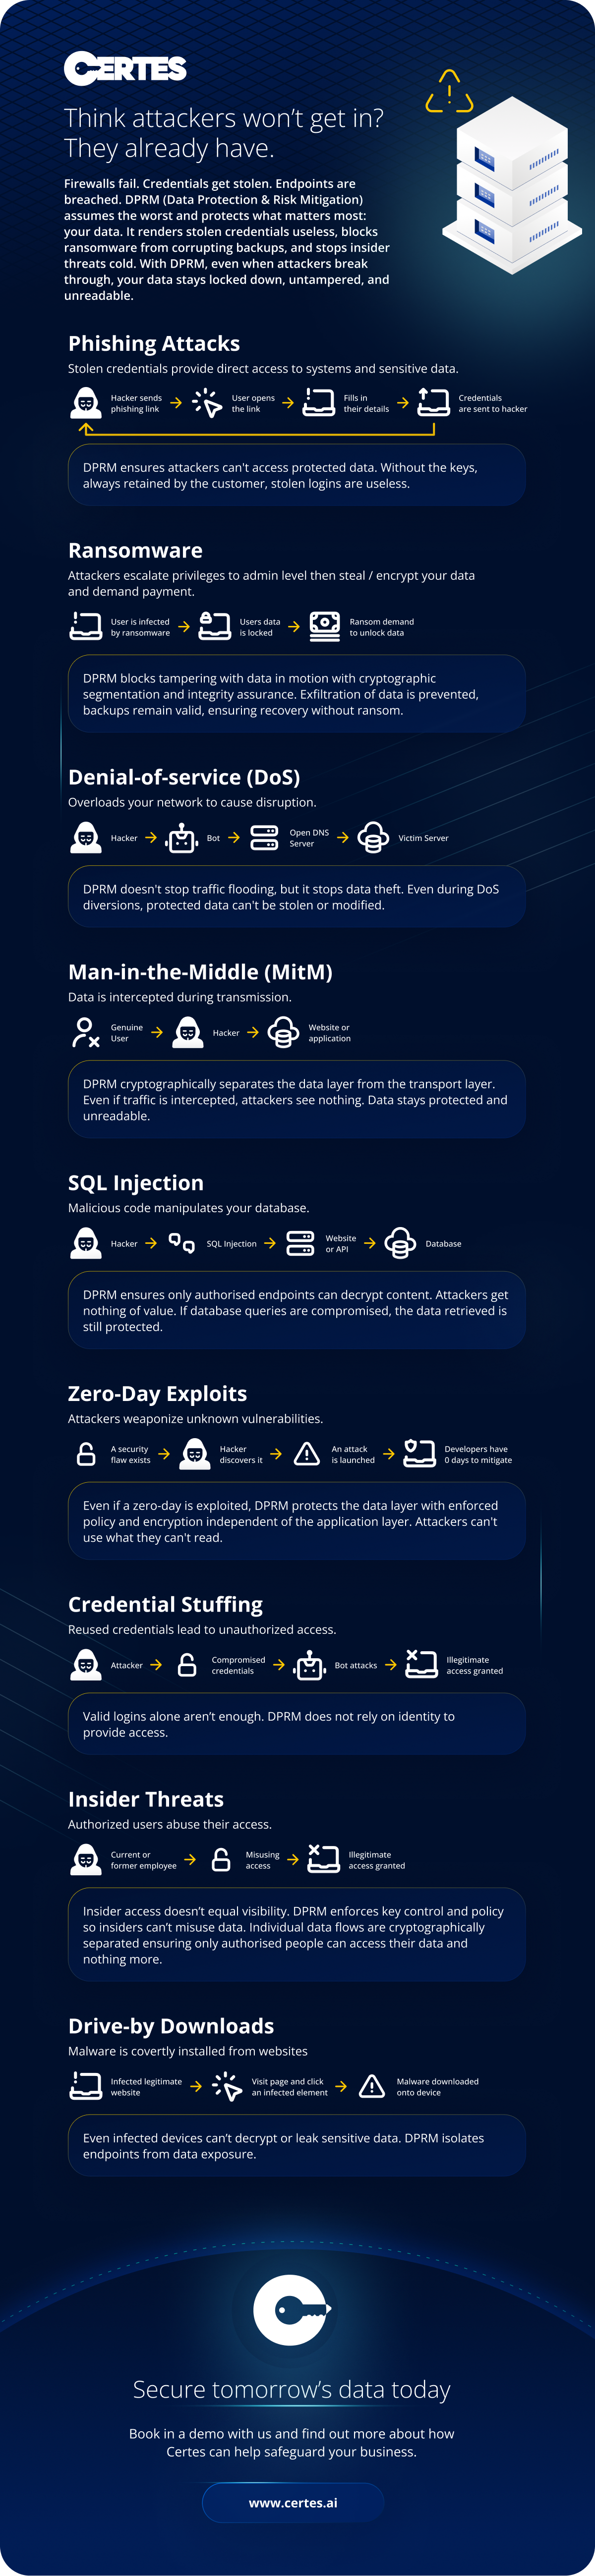
  • Think Attackers Won't Get In? They Already Have

    Infographic

    Think Attackers Won't Get In? They Already Have

    Firewalls fail. Credentials get stolen. Endpoints are breached. Cyber attackers use a range of sophisticated techniques to steal what's most important to you: your data. Here, we explain some of the most common types of cyber attack, and how Certes' DPRM (Data Protection & Risk Mitigation) protects your data so even when attackers break through, your data stays locked down, untampered, and unreadable.

Ready to protect the data that matters?

Talk to Certes about protecting sensitive data today.

Reduce exposure now, while your wider security and cryptographic transformation continues.